ISO 27001 advisory & independent audit
ISO 27001 consultancy and independent internal audit.
Build a working information security management system, understand your readiness for certification, or get an independent assessment of how your controls operate.
An introductory conversation to clarify your objectives and next step.
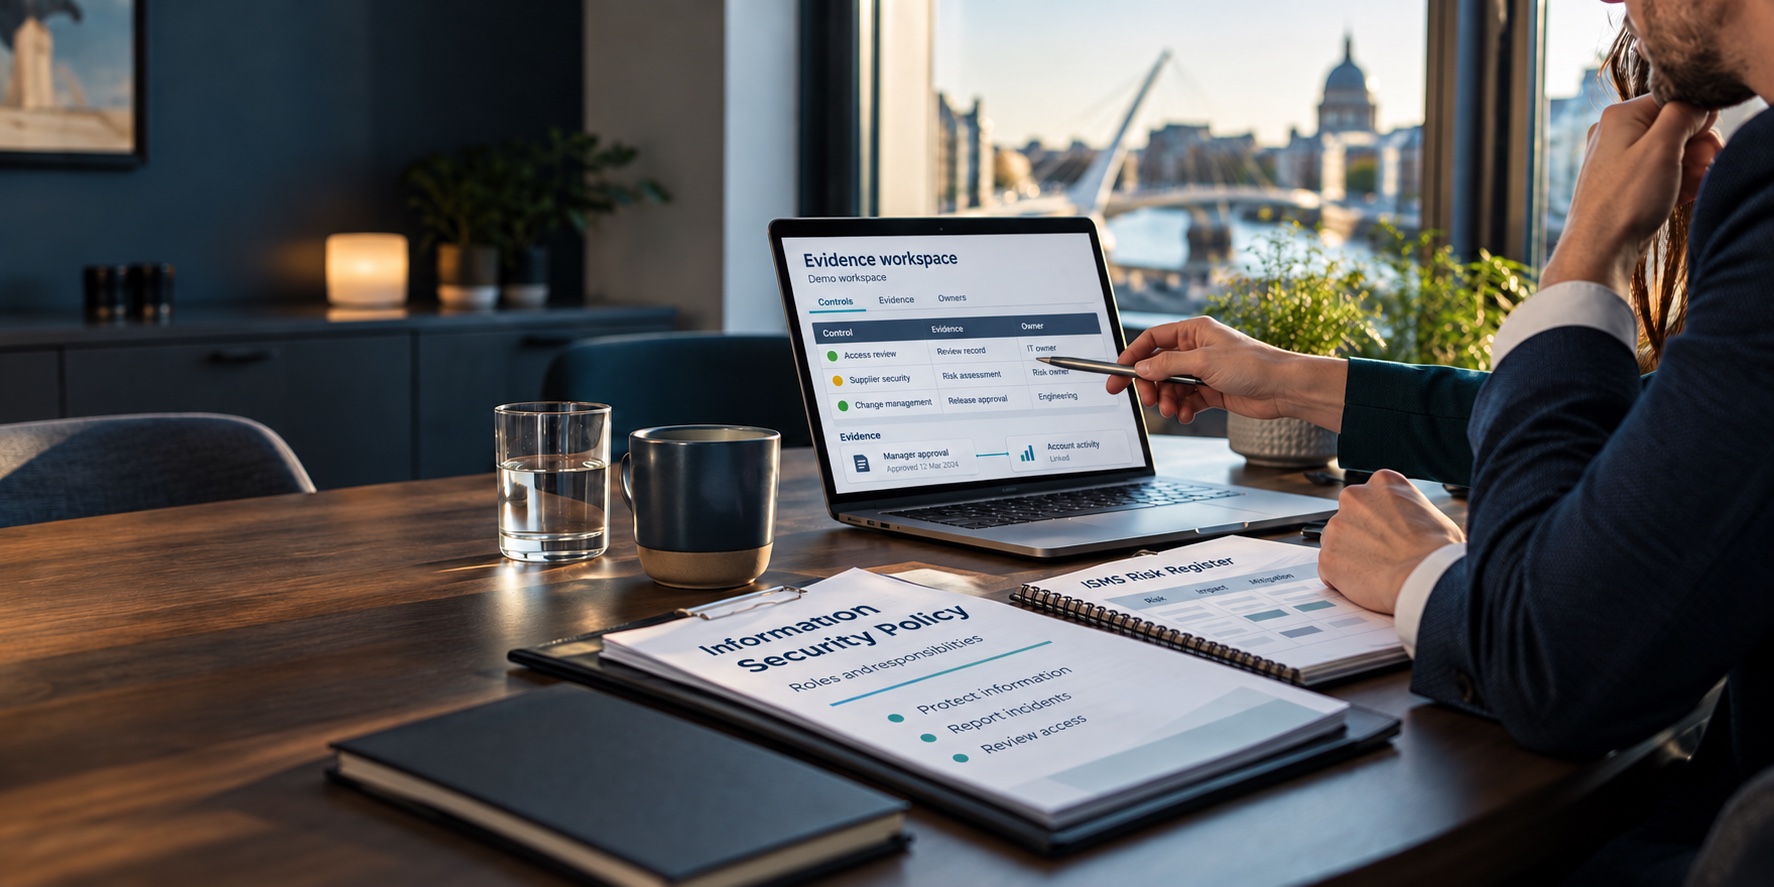
A policy in a folder is not a working control.
To be audit-ready, your team needs clear ownership, controls that operate in practice and records that show what happened. We help build that system—or independently test the evidence when it is time for an internal audit.
- 01 / DocumentedThe rule existsA policy sets the expectation.
- 02 / OwnedSomeone is accountableResponsibilities and decisions are clear.
- 03 / OperatingThe control happensPeople and systems follow the process.
- 04 / EvidencedThe record supports itSamples can be independently tested.
Core services
The right support for your next step.
Supplier and PIMS support is also available. See all services.
See the work
See how the work is documented.
Explore connected fictional report, workpaper and findings extracts. We can walk through the full pack during a scoping discussion.
Explore samplesRepresentative fictional samples — not historical client engagements.
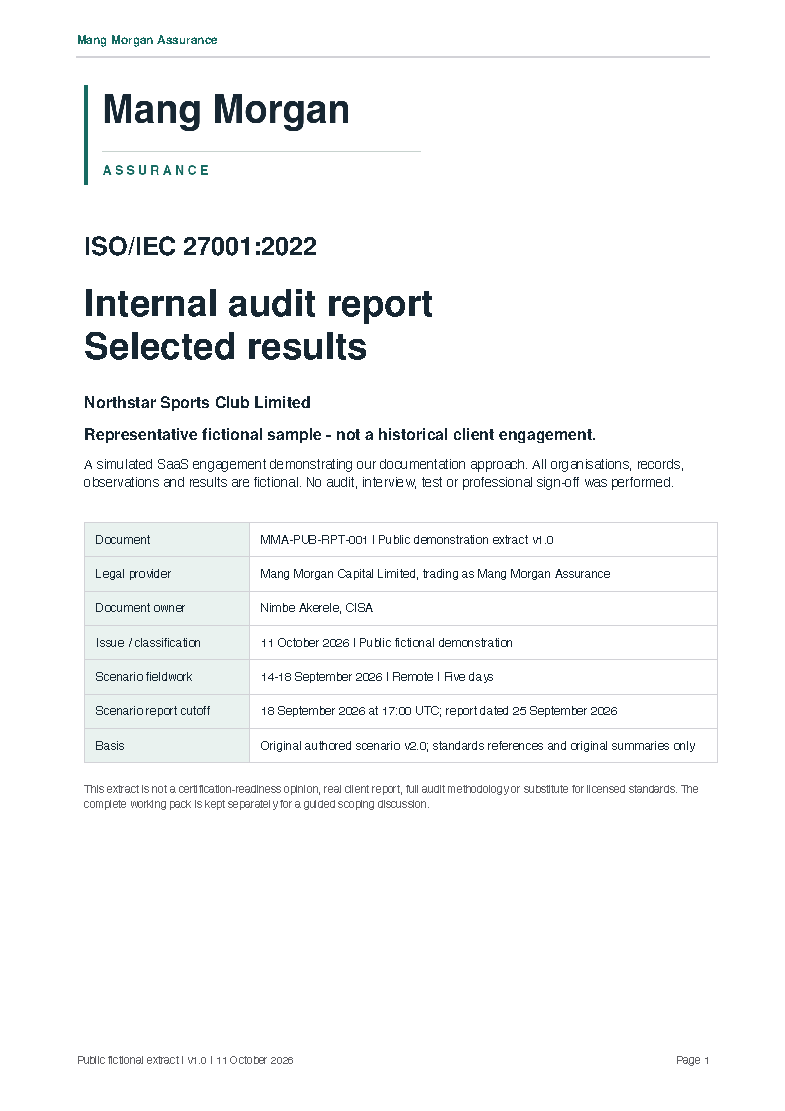 Audit report
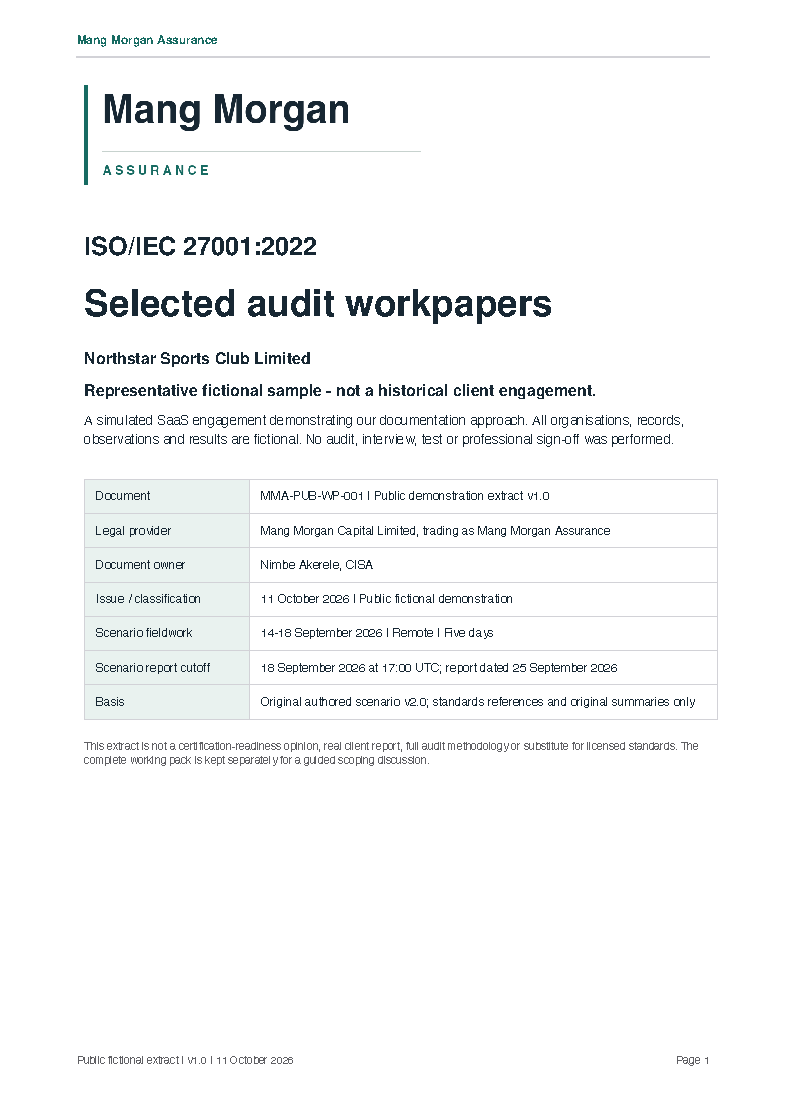 Workpapers
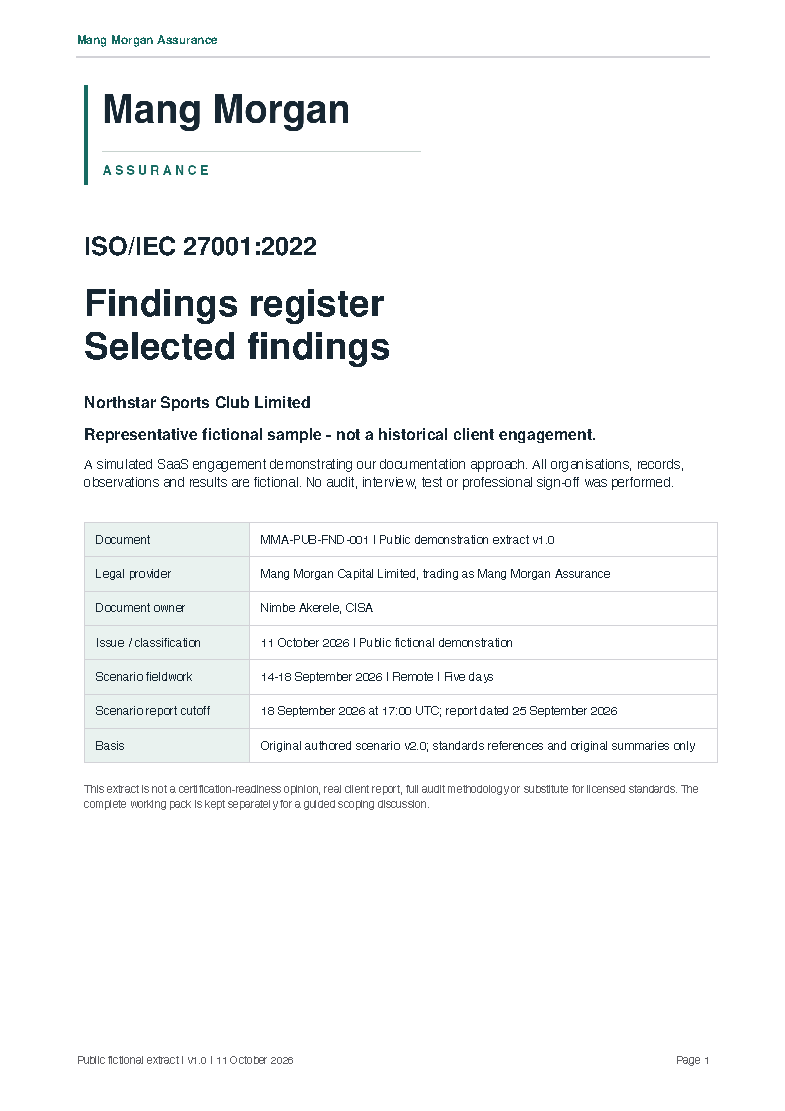 Findings
How we work
From uncertainty to a clear next step.
Every engagement follows an agreed route. What happens in delivery depends on whether you need advisory support or independent assurance.
- 01 / Understand
Start with your goal
We clarify the ISMS boundary, your target and what is already working.
You receive: a clear starting point - 02 / Agree
Define the work
We set scope, responsibilities, evidence access, timing and independence safeguards.
You receive: a scoped plan - 03 / Deliver
Build or test
Advisory: establish operating controls with your team.
Separate services. Clear ownership.
Assurance: independently test selected evidence. - 04 / Handover
Leave with a useful result
Receive an agreed roadmap or a traceable audit report, with follow-up scoped separately.
You receive: documented next steps
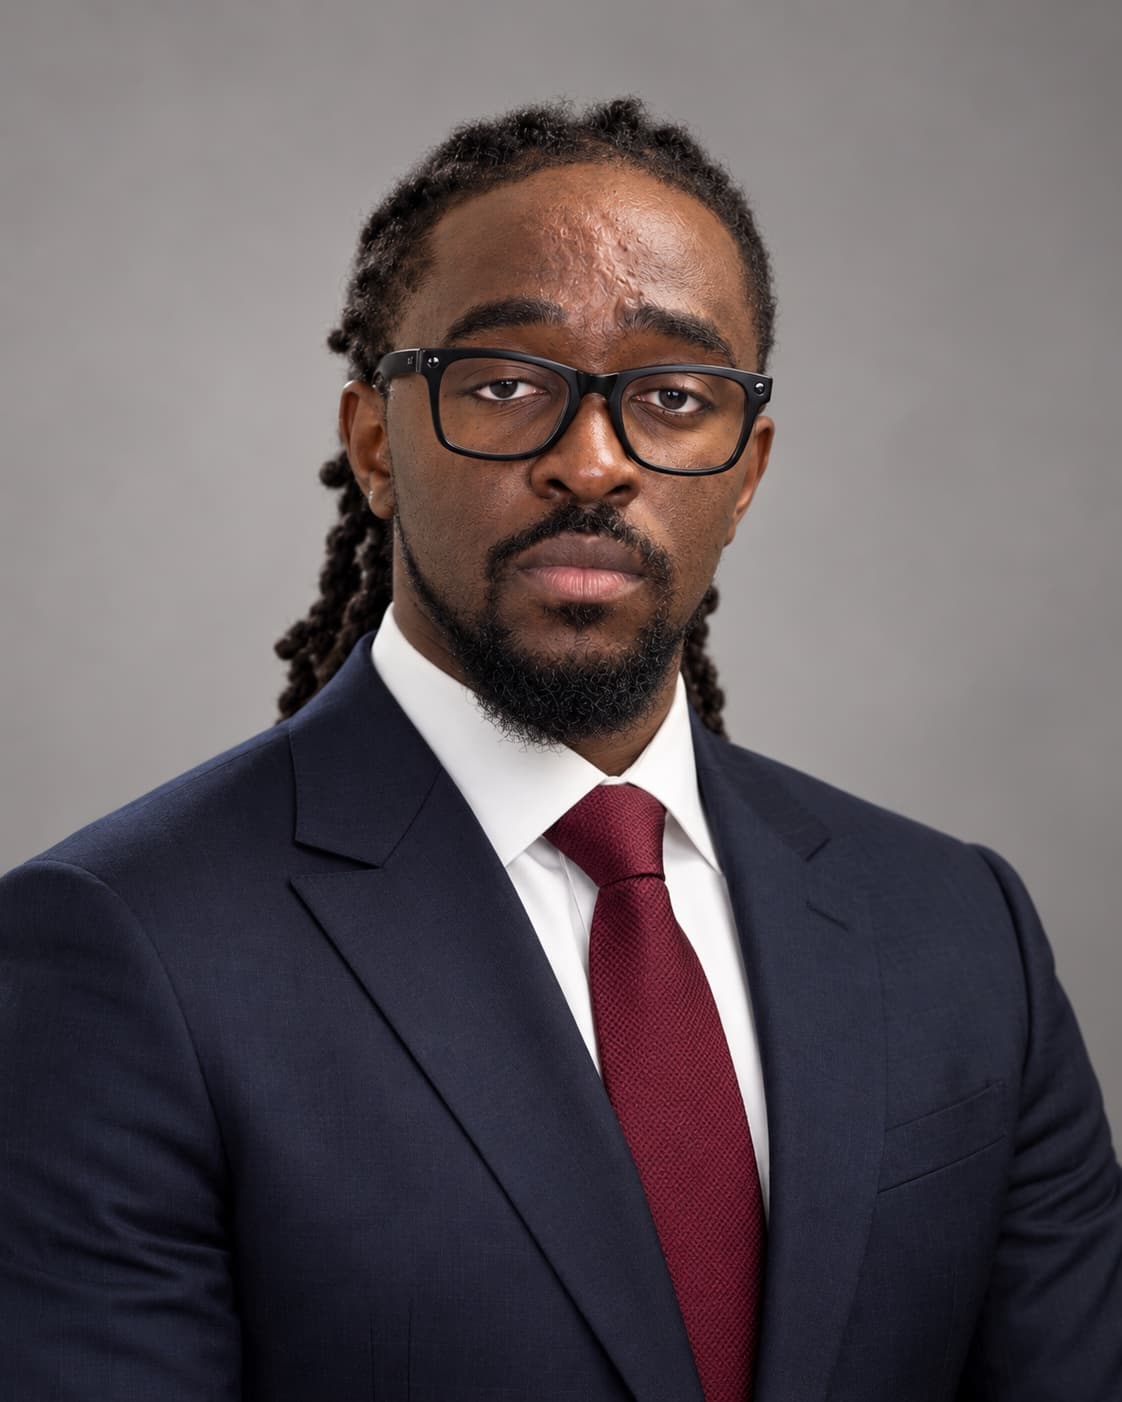
Meet the principal
Nimbe Akerele
Principal Auditor & Consultant
CISA and ISO/IEC 27001 Lead Auditor, with certification and internal-audit experience across growing technology organisations and large multinationals.
Experience leading audit teams and reviewing audit quality, with a practical understanding of security, privacy and technology risk.
Meet the people behind the practicePricing & scope
A quote built around your work.
We estimate delivery phases, roles and evidence readiness—not a generic price per control.
What shapes the fee?
Scope, evidence, interviews, testing depth and timetable.
What will the proposal show?
Deliverables, client inputs, assumptions, exclusions and payment milestones.
Common questions
Before we begin.
Short answers to the questions that matter when you are choosing support.
Do we need implementation, a readiness assessment or an internal audit?
Implementation helps establish an ISMS. A gap and readiness assessment clarifies what is missing or unproven. An internal audit independently tests an operating system against agreed criteria. We can help you choose the right starting point on a brief scope call.
Can Mang Morgan implement our ISMS and then audit it?
Not where we would be auditing our own work. Before acceptance, we check previous involvement and conflicts, record safeguards and assign an independent auditor or another provider where needed. If objectivity cannot be protected, we decline the independent audit. See our conflict checks and safeguards.
What will our team need to provide?
Start with your intended scope, target date and what is already in place. During delivery, you will need a sponsor and ISMS owner, access to process owners and a restricted way to share relevant evidence. We agree the commitment by phase.
How long will the work take and how is the fee set?
Both depend on scope, evidence readiness, interviews, testing depth and team availability. We estimate the work by phase and role, then show assumptions and payment terms in the proposal. See the pricing approach.
Can you work in Vanta, Drata or our GRC platform?
Yes, where your team authorises appropriate access. A platform can organise evidence, but its status indicators are not audit conclusions and do not automatically reduce the fee.
Will the work get us ISO 27001 certified?
No provider can guarantee certification. We support implementation and readiness or deliver an appropriately independent internal audit. Your chosen certification body makes the certification decision.
Start a conversation
Tell us your scope.
We will clarify the service, boundaries and timing before preparing a proposal.